

MD-102 Dumps PDF - MD-102 Real Exam Questions Answers
Get Started: MD-102 Exam [2026] Dumps Microsoft PDF Questions
Microsoft MD-102 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 156
You have SOO Windows 10 devices enrolled in Microsoft Intune.
You plan to use Exploit protection in Microsoft Intune to enable the following system settings on the devices:
* Data Execution Prevention (DEP)
* Force randomization for images (Mandatory ASlR)
You need to configure a Windows 10 device that will be used to create a template file.
Which protection areas on the device should you configure in the Windows Security app before you create the template file? To answer, drag the appropriate protection areas to the correct settings. Each protection area may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 157
You have a Microsoft Intune subscription.
You have devices enrolled in intune as shown in the following table.
An app named App1 is installed on each device.
What is the minimum number of app configuration policies required to manage Appl ?
- A. 0
- B. 1
- C. 2
- D. 3
- E. 4
Answer: D
Explanation:
The correct answer is B because you need to create two app configuration policies for managed devices, one for iOS/iPadOS devices and one for Android devices1. App configuration policies let you customize the settings of apps for iOS/iPadOS or Android devices1. The settings are assigned to user groups and applied when the app runs1. The app developer or supplier provides the configuration settings (keys and values) that are exposed to Intune1. You can't use a single app configuration policy for both iOS/iPadOS and Android devices because they have different configuration settings2. References: 1: App configuration policies for Microsoft Intune | Microsoft Learn
https://learn.microsoft.com/en-us/mem/intune/apps/app-configuration-policies-overview 2: Add app configuration policies for managed iOS/iPadOS devices | Microsoft Learn
https://learn.microsoft.com/en-us/mem/intune/apps/app-configuration-policies-use-ios
NEW QUESTION # 158
You have a Microsoft 365 subscription that contains 1,000 Windows 11 devices enrolled in Microsoft Intune.
You plan to create and monitor the results of a compliance policy used to validate the BIOS version of the devices.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - Create a PowerSheel discovery script and a JSON file.
2 - Upload the PowerShell script to Intune.
3 - Upload the JSON file to Azure AD.
4 - Create and assign a custom compliance policy.
NEW QUESTION # 159
Your company has computers that run Windows 10 and are Microsoft Azure Active Directory (Azure AD)-joined.
The company purchases an Azure subscription.
You need to collect Windows events from the Windows 10 computers in Azure. The solution must enable you to create alerts based on the collected events.
What should you create in Azure and what should you configure on the computers? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/azure-monitor/platform/log-analytics-agent
NEW QUESTION # 160
You have computers that run Windows 10 and are configured by using Windows AutoPilot.
A user performs the following tasks on a computer named Computer1:
Creates a VPN connection to the corporate network
Installs a Microsoft Store app named App1
Connects to a Wi-Fi network
You perform a Windows AutoPilot Reset on Computer1.
What will be the state of the computer when the user signs in? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/deployment/windows-autopilot/windows-autopilot-reset
NEW QUESTION # 161
Your network contains an Active Directory domain named adatum.com, a workgroup, and computers that run Windows 10. The computers are configured as shown in the following table.
The local Administrator accounts on Computed, Computed, and Computed have the same user name and password.
On Computed. Windows Defender Firewall is configured as shown in the following exhibit.

Answer:
Explanation:
Explanation:
NEW QUESTION # 162
You have a Microsoft 365 subscription.
You need provide a user the ability to disable Security defaults and principle of least privilege.
Which role should you assign to the user?
- A. Security Administrator
- B. Global Administrator
- C. Intune Administrator
- D. Conditional Access Administrator
Answer: D
Explanation:
To enable or disable security defaults in your directory, sign in to theAzure portalas a security administrator, Conditional Access administrator, or global administrator.
Note: Conditional Access Administrator
Users with this role have the ability to manage Azure Active Directory Conditional Access settings.
Reference:https://docs.microsoft.com/en-us/azure/active-directory/fundamentals/concept-fundamentals-security-
NEW QUESTION # 163
You have a Microsoft 365 subscription.
You use Microsoft Intune Suite to manage devices.
You have the iOS app protection policy shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic. NOTE: Each correct selection is worth one point,
Answer:
Explanation: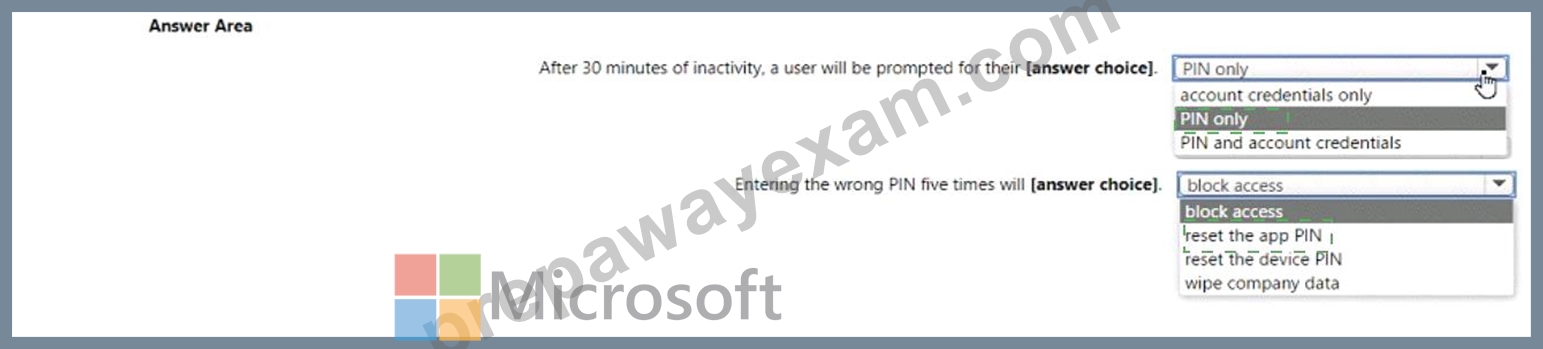
Explanation
Box 1 = PIN only
Box 2 = reset the PIN app
iOS/iPadOS app protection policy settings - Microsoft Intune | Microsoft Learn
https://learn.microsoft.com/en-us/mem/intune/apps/app-protection-policy-settings-ios
NEW QUESTION # 164
You have a Microsoft 365 tenant that contains the devices shown in the following table.
The devices are managed by using Microsoft Intune.
You create a compliance policy named Policy1 and assign Policy1 to Group1. Policy1 is configured to mark a device as Compliant only if the device security settings match the settings specified in the policy.
You discover that devices that are not members of Group1 are shown as Compliant.
You need to ensure that only devices that are assigned a compliance policy can be shown as Compliant. All other devices must be shown as Not compliant.
What should you do?
- A. From Policy1, modify the actions for noncompliance.
- B. From Tenant administration, modify the Diagnostic settings.
- C. From Endpoint security, configure the Conditional access settings.
- D. From Device compliance, configure the Compliance policy settings.
Answer: D
Explanation:
There are two parts to compliance policies in Intune:
Compliance policy settings - Tenant-wide settings that are like a built-in compliance policy that every device receives. Compliance policy settings set a baseline for how compliance policy works in your Intune environment, including whether devices that haven't received any device compliance policies are compliant or noncompliant.
Device compliance policy - Platform-specific rules you configure and deploy to groups of users or devices. These rules define requirements for devices, like minimum operating systems or the use of disk encryption. Devices must meet these rules to be considered compliant.
Reference:
https://docs.microsoft.com/en-us/mem/intune/protect/device-compliance-get-started
NEW QUESTION # 165
You have devices enrolled in Microsoft Intune as shown in the following table.
Intune includes the device compliance policies shown in the following table.
The device compliance policies have the assignments shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Device1 is marked as compliant = No Device2 is marked as compliant = Yes Device3 is marked as compliant
= No
Device1 is marked as noncompliant because it does not meet the minimum OS version requirement of Policy1, which is 11.0.0. Device1 has an OS version of 10.0.0, which is lower than the required version1.
Device2 is marked as compliant because it meets all the requirements of Policy2, which are: minimum OS version of 10.0.0, password required, and encryption enabled. Device2 has an OS version of 11.0.0, a password set, and encryption enabled1.
Device3 is marked as noncompliant because it does not meet the encryption requirement of Policy3, which is enabled. Device3 has encryption disabled1.
NEW QUESTION # 166
Hotspot Question
Your company uses Microsoft Endpoint Configuration Manager and purchases a Microsoft 365 subscription.
You need to set up Desktop Analytics.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: The Microsoft Endpoint Manager console
How to set up Desktop Analytics.
Use this procedure to sign in to Desktop Analytics and configure it in your subscription. This procedure is a one-time process to set up Desktop Analytics for your organization.
Initial onboarding
1. Open the Desktop Analytics portal in the Microsoft Endpoint Manager admin center as a user with the Global Admin role. Select Start. Alternatively, on the Configuration Manager console, go to the Software Library workspace, select the Desktop Analytics Servicing node, and select Plan deployments.
2. Etc.
Box 2: Configure Azure Services
Use this procedure to connect Configuration Manager to Desktop Analytics, and configure device settings. This procedure is a one-time process to attach your hierarchy to the cloud service.
In the Configuration Manager console, go to the Administration workspace, expand Cloud Services, and select the Azure Services node. Select Configure Azure Services in the ribbon.
Reference:
https://docs.microsoft.com/en-us/mem/configmgr/desktop-analytics/connect-configmgr
https://docs.microsoft.com/en-us/mem/configmgr/desktop-analytics/set-up
NEW QUESTION # 167
You have a Microsoft 365 subscription.
You plan to use Windows Autopilot to provision 25 Windows 11 devices.
You need to configure the Out-of-box experience (OOBE) settings.
What should you create in the Microsoft Intune admin center?
- A. an enrollment status page (ESP)
- B. a deployment profile
- C. a compliance policy
- D. a configuration profile
- E. a PowerShell script
Answer: B
NEW QUESTION # 168
Hotspot Question
You have a Microsoft 365 E5 subscription that contains a user named User1.
You need to perform the following tasks for User1:
- Set the Usage location to Canada.
- Configure the Phone and Email authentication contact info for self-service password reset (SSPR).
Which two settings should you configure in the Azure Active Directory admin center? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Profile - https://connectioncloudsupport.zendesk.com/hc/en-us/articles/4405103699865-How-to- update-UsageLocation-user-setting-in-Azure-AD Auth methods - https://learn.microsoft.com/en-us/azure/active-directory/authentication/concept- authentication-phone-options
NEW QUESTION # 169
You have a Microsoft 365 subscription that uses Microsoft Intune Suite.
You use Microsoft Intune to manage devices.
You use Windows Autopilot to deploy Windows 11 to devices.
A support engineer reports that when a deployment fails, they cannot collect deployment logs from failed device.
You need to ensure that when a deployment fails, the deployment logs can be collected.
What should you configure?
- A. the enrollment status page (ESP) profile
- B. the automatic enrollment settings
- C. the Windows Autopilot deployment profile
- D. the device configuration profile
Answer: A
Explanation:
https://learn.microsoft.com/en-us/autopilot/enrollment-status#esp-profiles
NEW QUESTION # 170
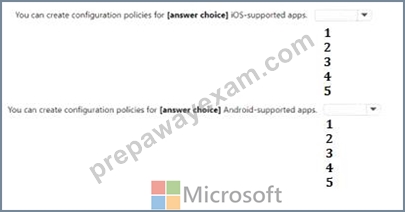
You have a Microsoft 365 ES subscription that uses Microsoft Intune.
You have the apps shown in the following exhibit.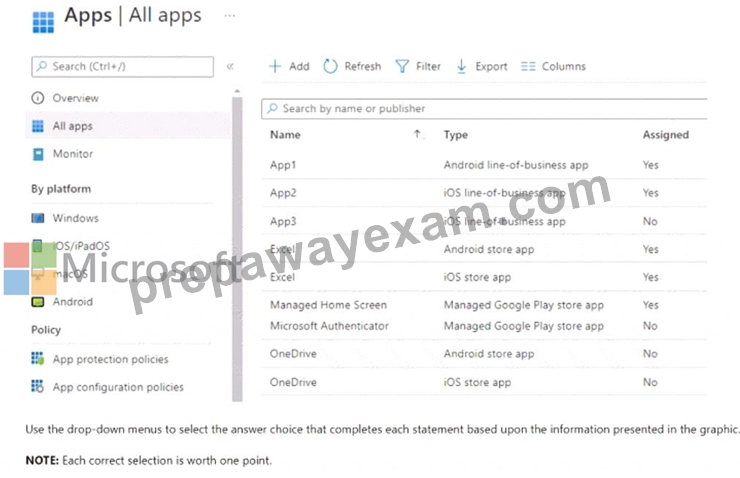
Answer:
Explanation:
Explanation:
NEW QUESTION # 171
Hotspot Question
Your network contains an Active Directory domain.
The domain contains computers that run Windows 10 and are enrolled in Microsoft Intune.
Updates are deployed by using Windows Update for Business.
Users in a group named Group1 must meet the following requirements:
- Update installations must occur any day only between 00:00 and 05:00.
- Updates must be downloaded from Microsoft and from other company
computers that already downloaded the updates.
You need to configure the Windows 10 Update Rings in Intune to meet the requirements.
Which two settings should you modify? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Notify download
Here's what Automatic update behavior means:
* Notify download" Notify the user before downloading the update. Users choose to download and install updates.
* Auto install at maintenance time" Updates download automatically and then install during Automatic Maintenance when the device isn't in use or running on battery power.
* Auto install and restart at maintenance time Updates download automatically and then install during Automatic Maintenance when the device isn't in use or running on battery power.
Box 2: Not configured
With Intune, use Delivery Optimization settings for your Windows devices to reduce bandwidth consumption when those devices download applications and updates. Configure Delivery Optimization as part of your device configuration profiles.
Reference:
https://deviceadvice.io/2020/01/27/windows-10-update-rings-the-best-user-experience/
https://docs.microsoft.com/en-us/intune/delivery-optimization-windows#move-from-existing- update-rings-to-delivery-optimization
NEW QUESTION # 172
You have a Microsoft 365 subscription that uses Microsoft Intune and contains the users shown in the following table.
Group2 has been assigned in the Enrollment Status Page.
You have the devices shown in the following table.
You capture and upload the hardware IDs of the devices in the marketing department.
You configure Windows Autopilot.
For each of the following statements, select Yes if the statement is true. Otherwise select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 173
......
MD-102 Premium Exam Engine pdf Download: https://itcertspass.prepawayexam.com/Microsoft/braindumps.MD-102.ete.file.html